Secure research data sharing
Secure research data sharing you can take back
Partnering and in-licensing both involve letting someone outside your company read confidential work for a while. Molecule Labs shares confidential files only with named members, encrypts them before they leave your device, and lets you revoke access at any time.
What a collaborator sees
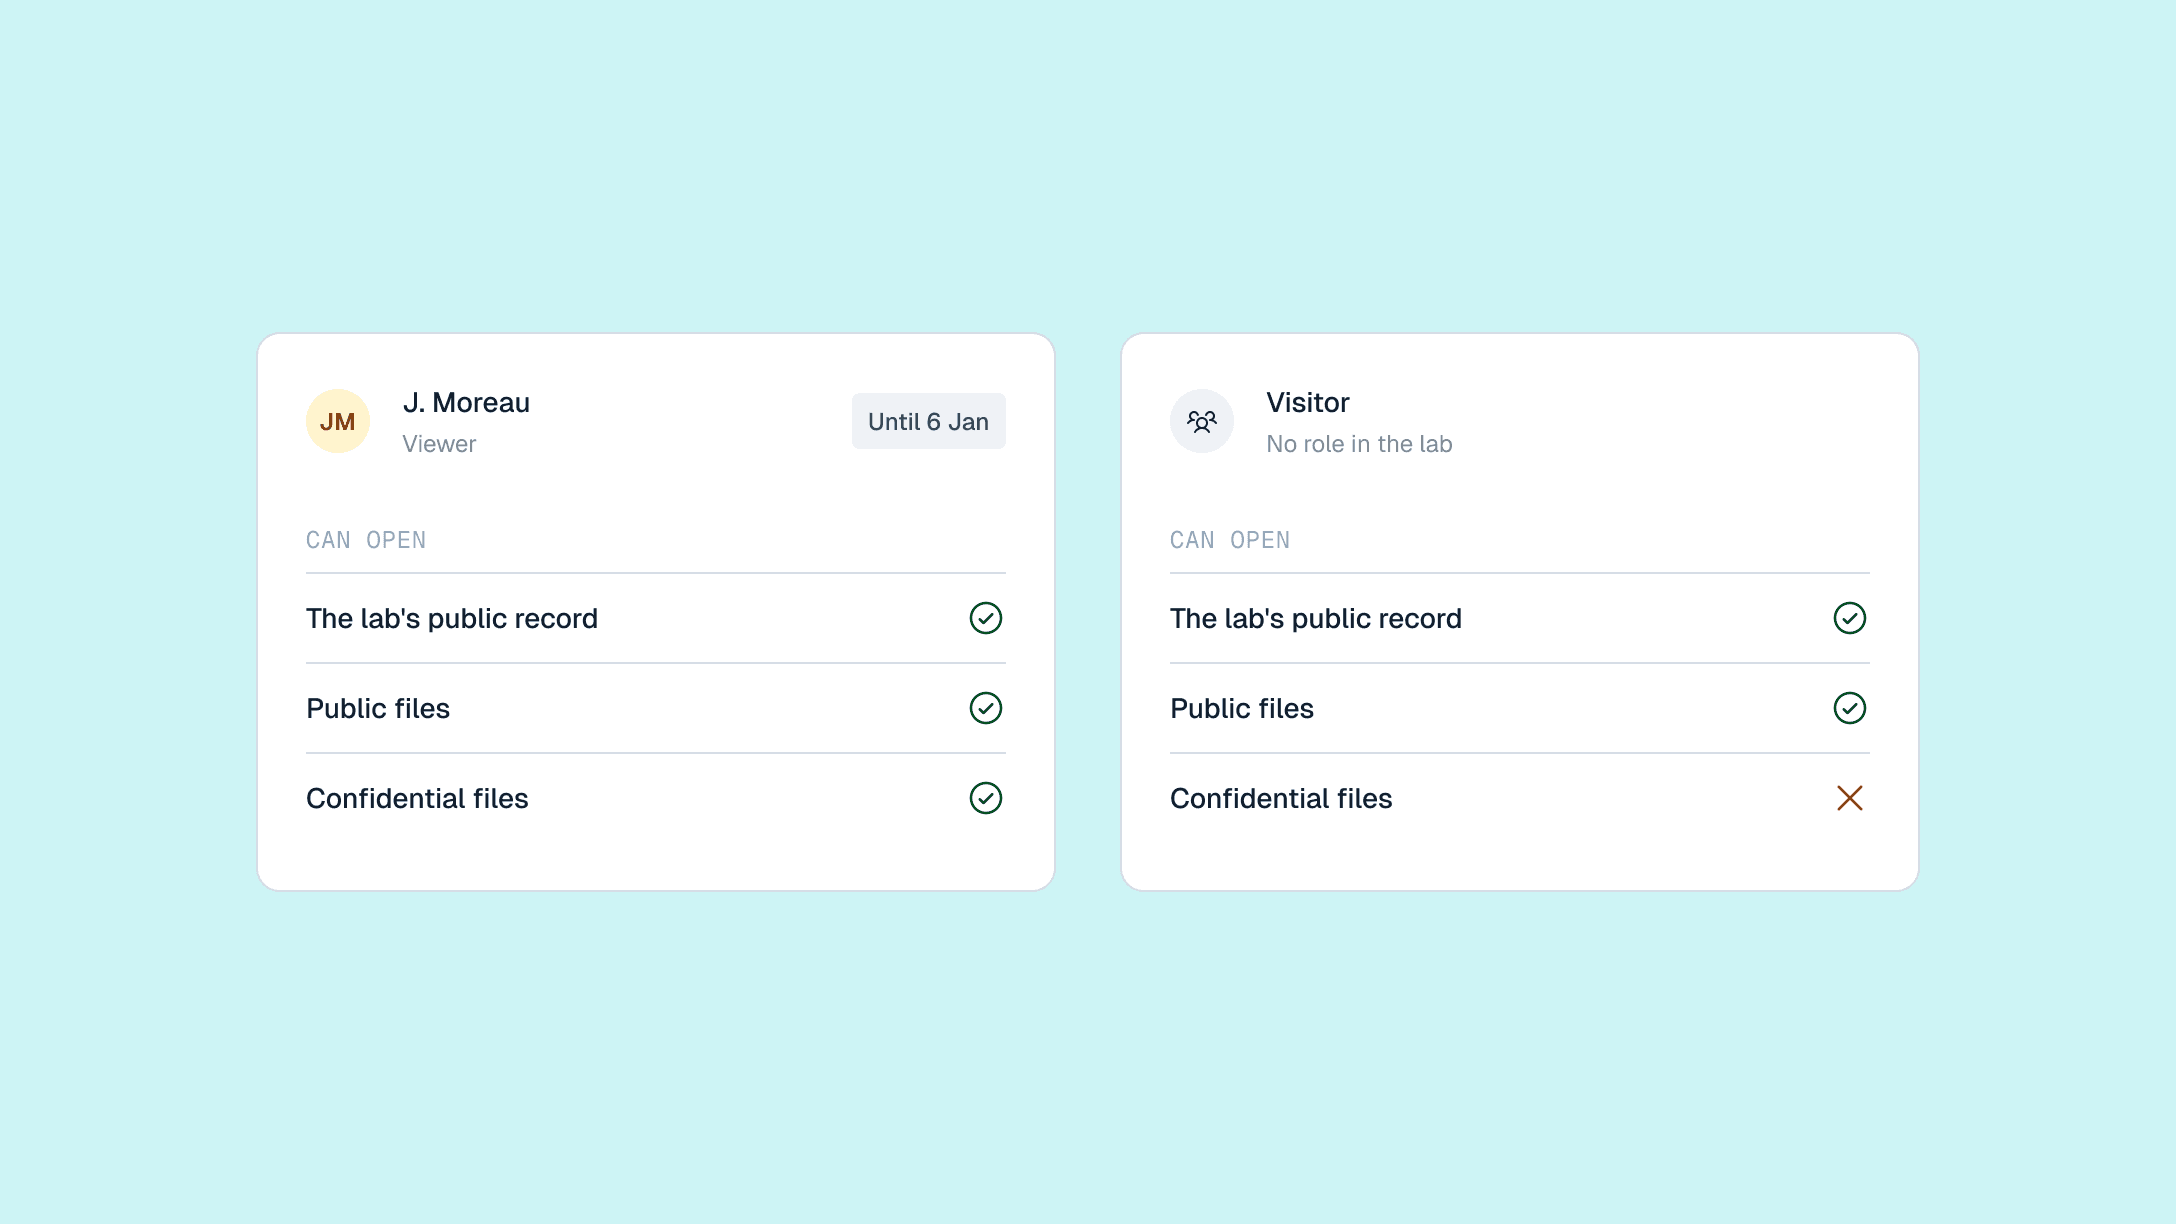
Role-based access means you can choose who sees what
How a collaborator gets in, and out
Role-based access with time limits
Decide what they need to do
Read-only if they only need to look, including at confidential files. Contributor if they need to add work of their own.
Grant it with an end date
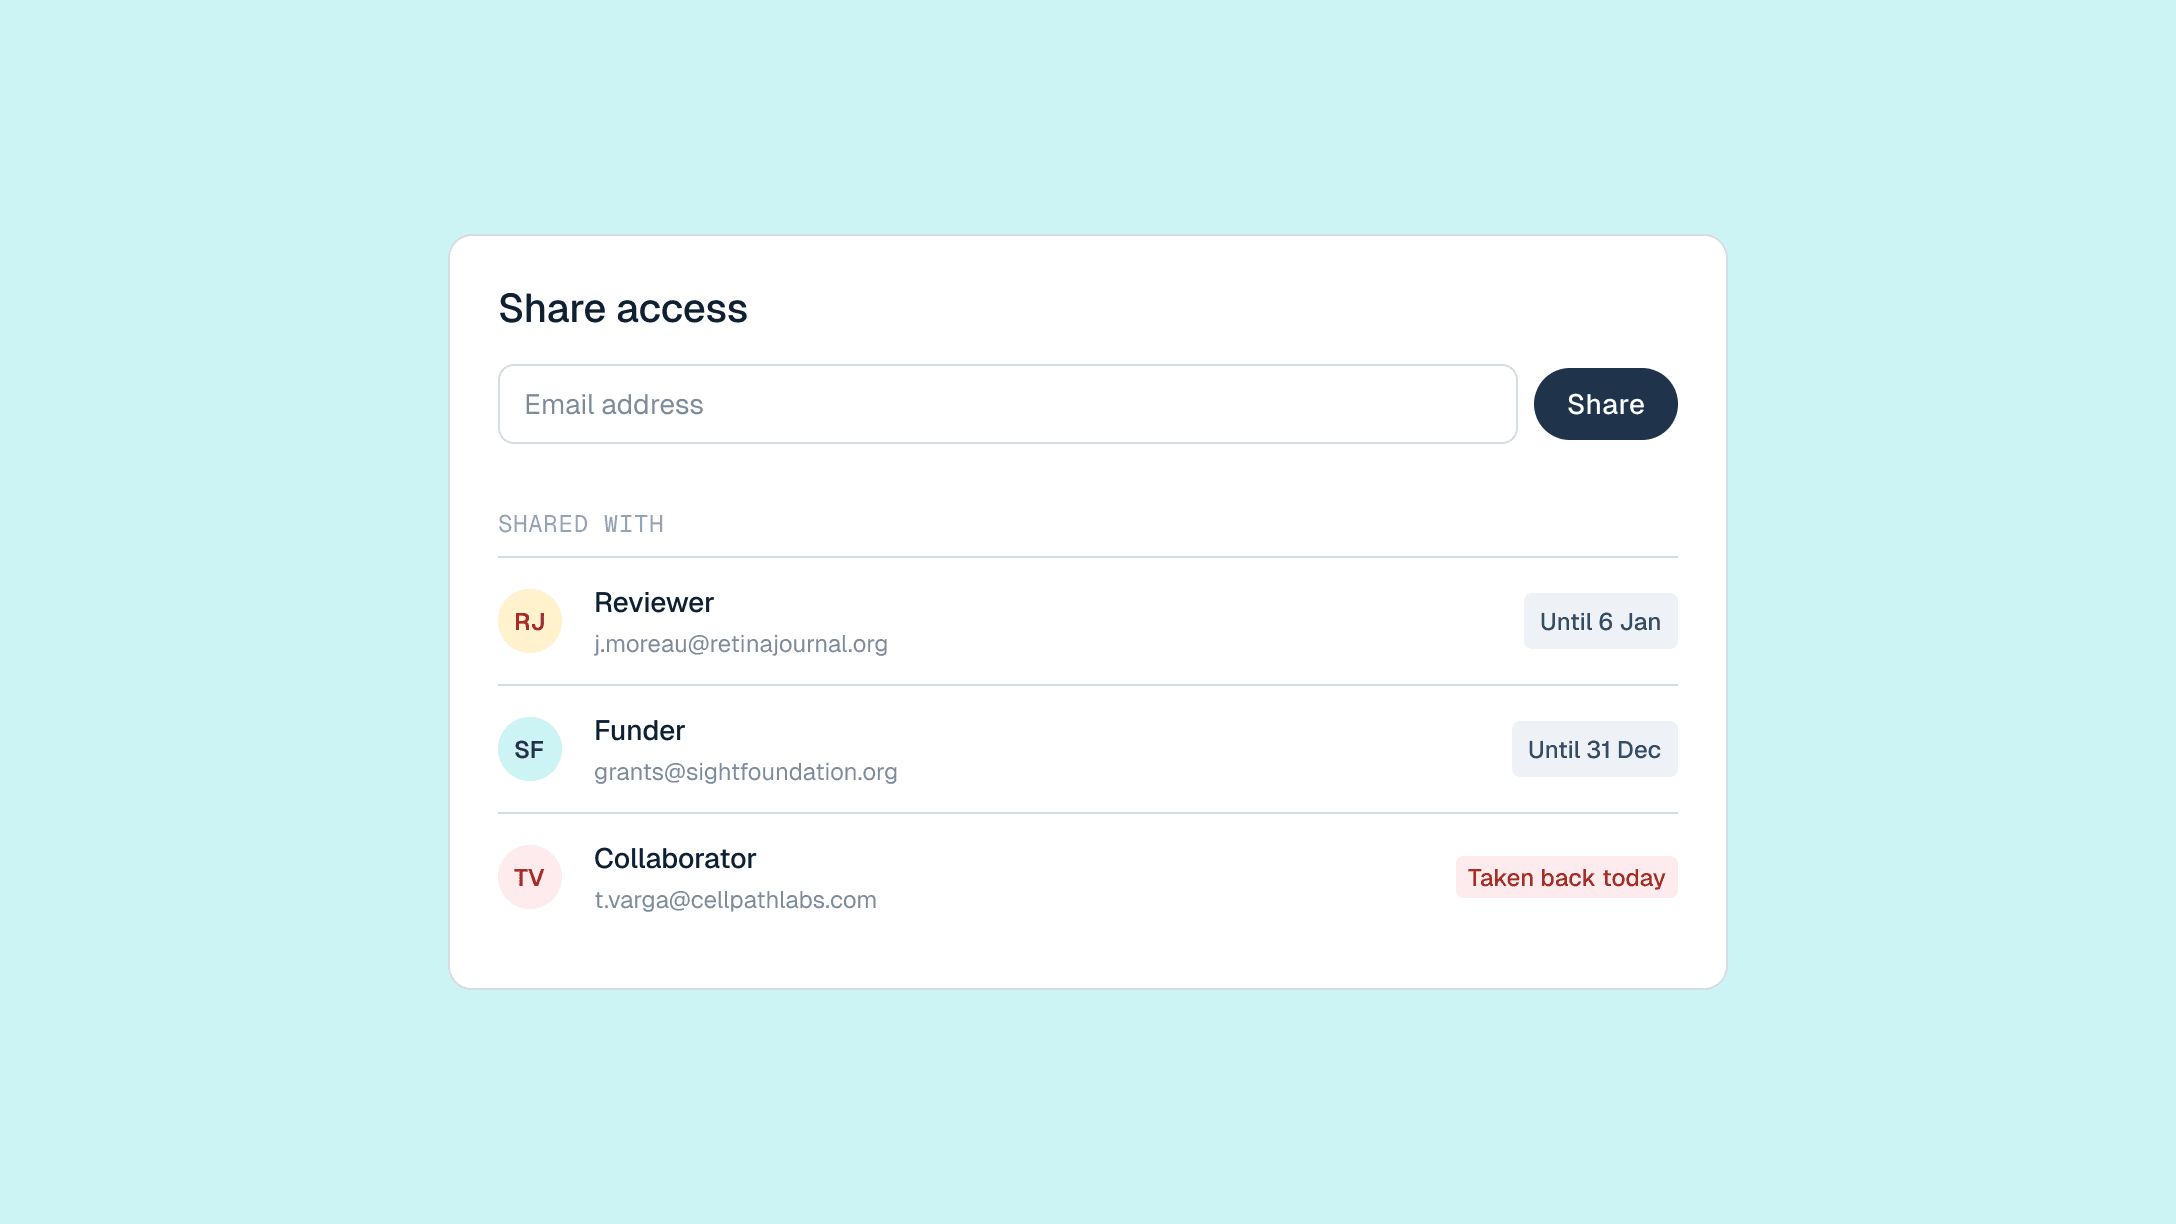
When you grant access you can add time limits. Nobody has to remember to clean up after the project ends.
They open what they were given
Access is re-checked on each open. Decryption of the file happens every time.
You take it back when it is over
Revoking ends access going forward. What they contributed stays part of the Lab's record.
What makes secure research data sharing different from a private link
Most tools protect the transfer but can't assure time-boxed access. Instead of running down legacy links, Molecule Labs can control access from one portal.
Confidential files are encrypted before they leave the device
A confidential file is unreadable before it travels. What reaches storage is already locked, so a readable copy never sits on our servers.
Access is named, not a link
People are granted access as members with a role. There is no link that works for whoever happens to hold it, and a Viewer can't pass access on to anyone else.
Permissions end
A permission can carry an end date, and it can be revoked before then. Access is checked each time a file is opened rather than at the moment it was shared.
Every share leaves a record
Who was given access, at what level, and when it ended are all part of the Lab's history. When a team member asks who else has seen this, the answer is retrievable rather than remembered.
Add, remove and modify roles at any time