Security and Permissions
Protecting scientific data
Every file you mark confidential in Molecule Labs is encrypted before it reaches our servers, and only the people granted access can open it. Access is given deliberately, and it can be changed or revoked at any time.
How our encryption works
We use the same class of encryption that protects banking and government data. Encryption makes a file unreadable to anyone without the key, and access rules decide exactly who holds that key.
Confidential files are encrypted on the device
The moment a confidential file is uploaded, it's scrambled into unreadable ciphertext right in the browser, before it travels anywhere. What reaches our storage is already locked. At no point in the journey does a readable copy sit on Molecule's servers.
The key is tied to access rules
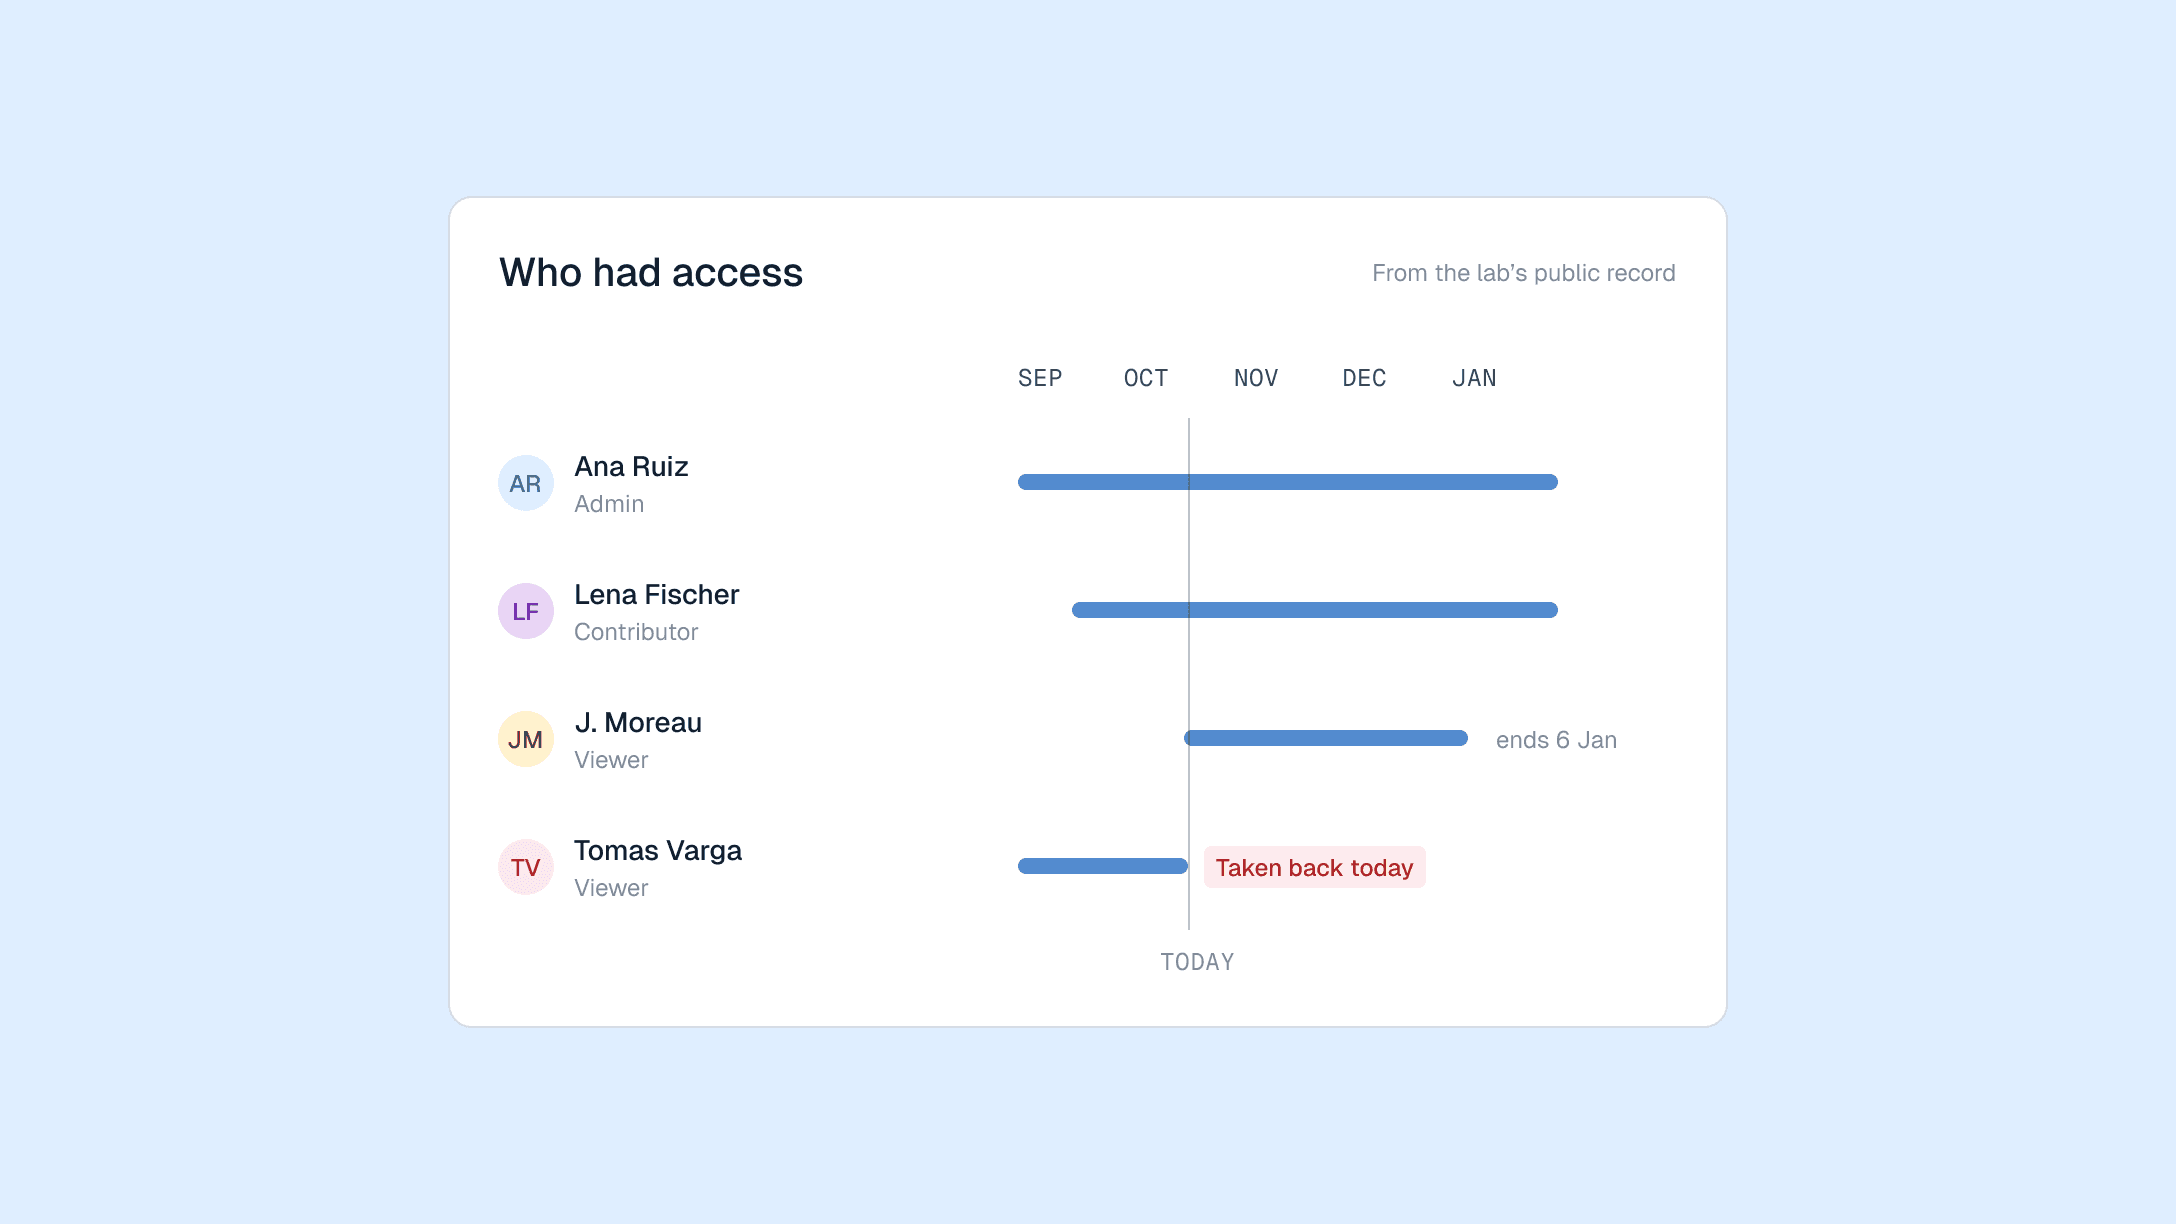
Opening a confidential file requires a key, and that key is released only to members whose role allows it. Every role given or taken back is recorded with its date on the lab's public record.
Access is checked every single time
Permissions are a living system. Every time someone opens a file, their access is re-checked against the current rules.
Role-based access
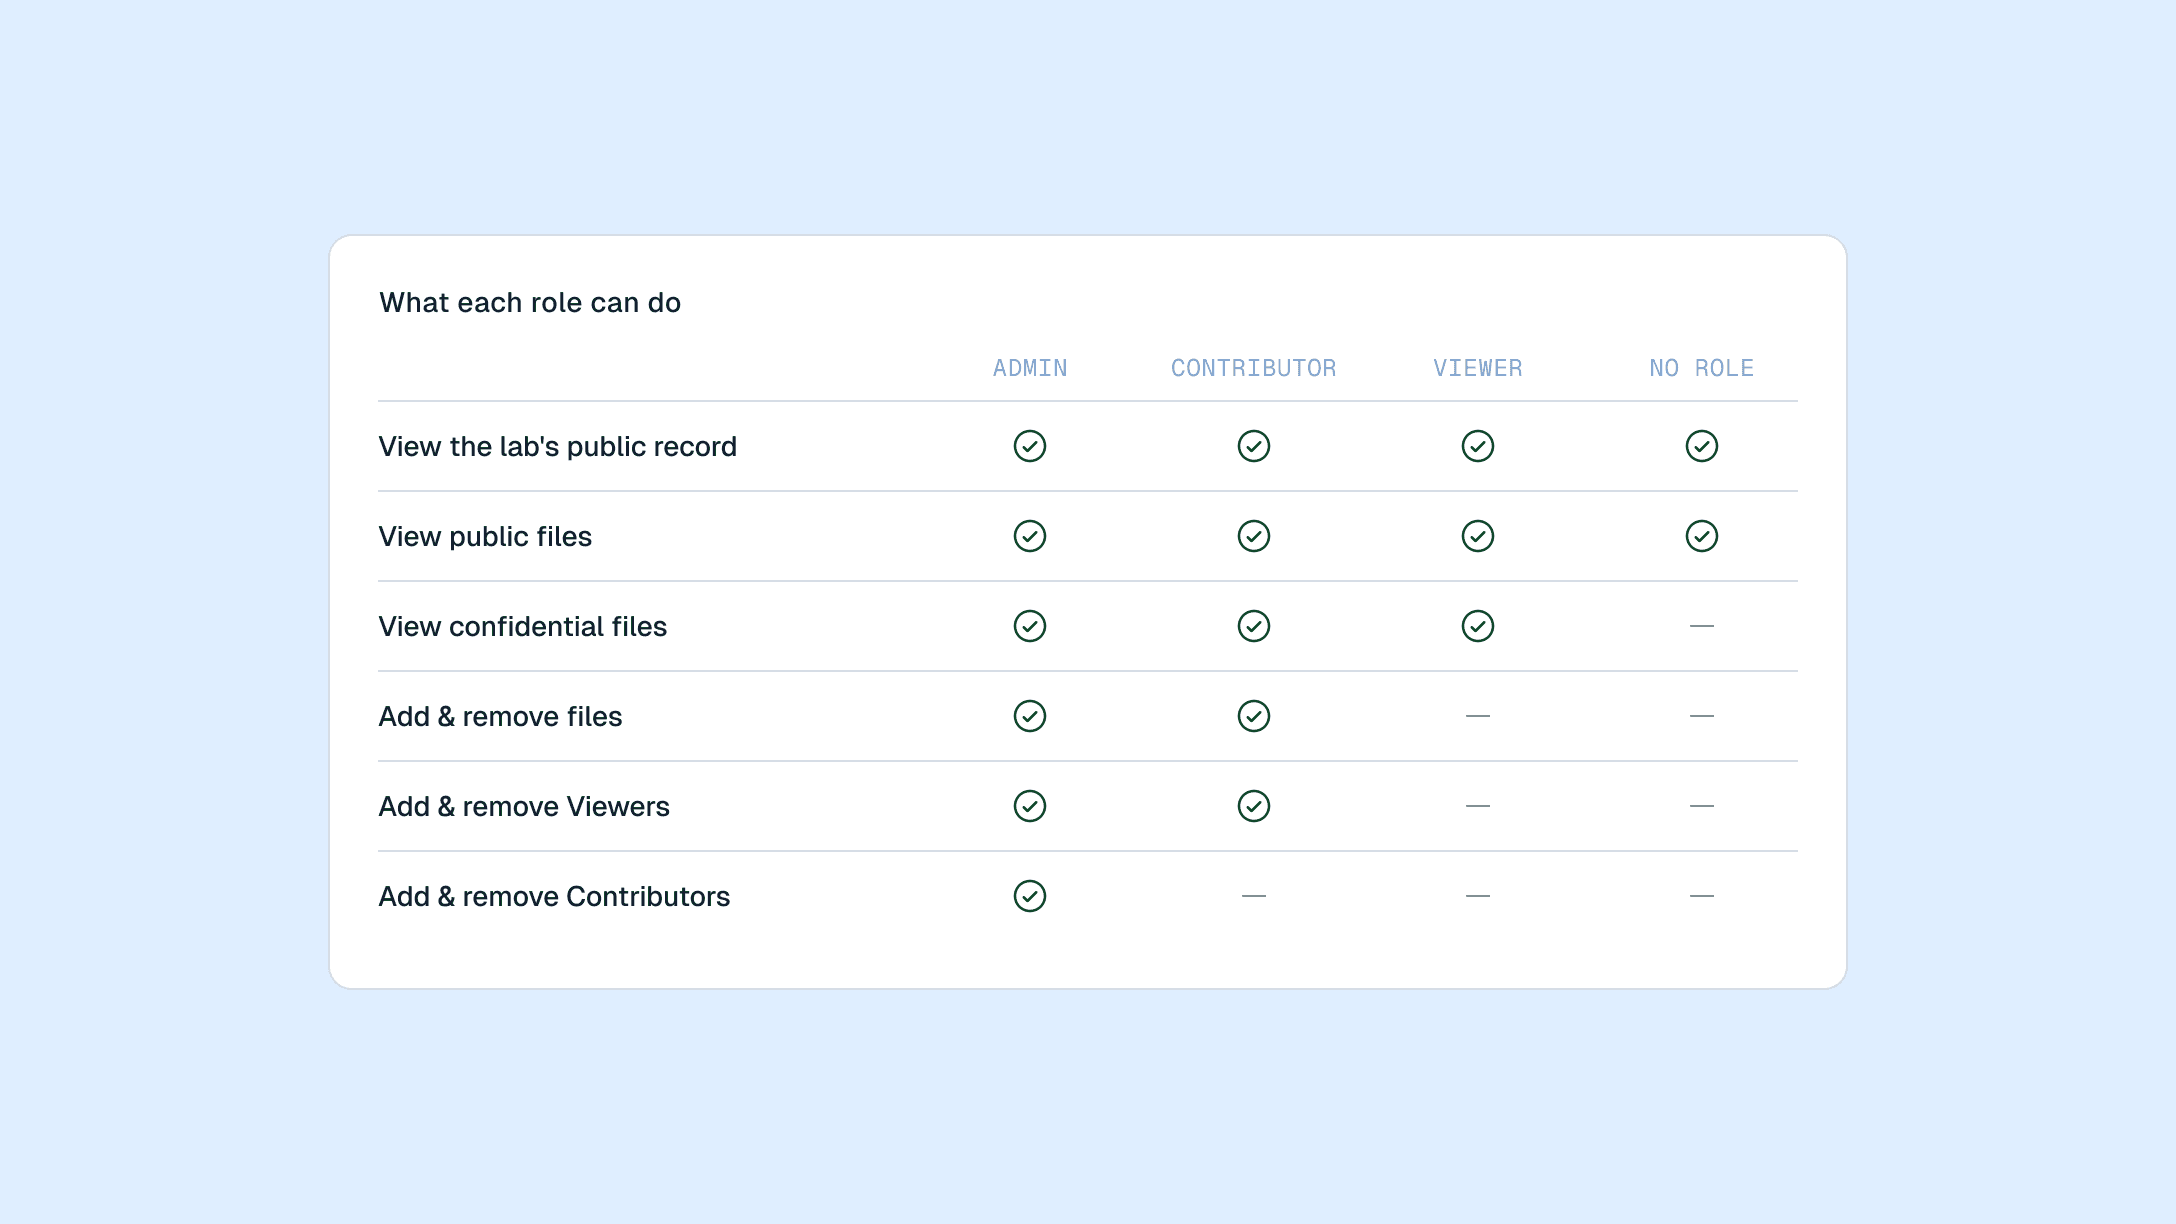
Add, remove, and timebox users